360° Security and Penetration Testing Services

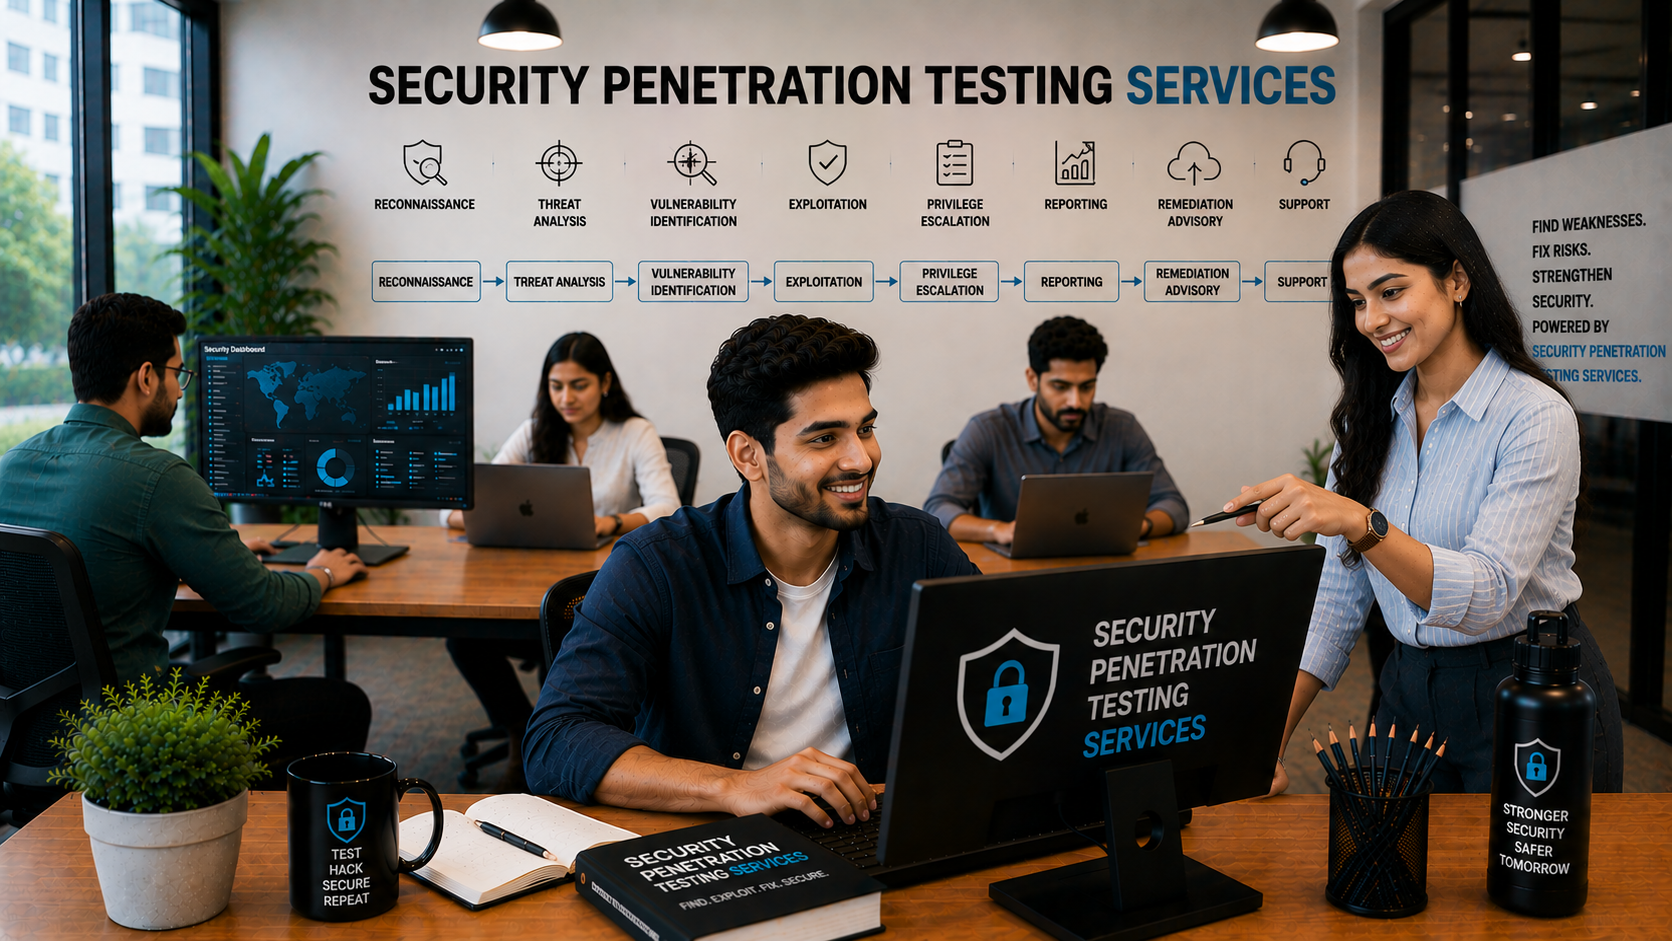
Enhance your system safety to improve customer satisfaction
A controlled security assessment with usable findings
Agree scope and authorisation
Understand the attack surface
Test and verify carefully
Support remediation
Clear Security Findings With Practical Remediation Guidance
Application Security Assessment
Evaluate exposed functionality, authentication, permissions and common application vulnerabilities.
Verified Risk Reporting
Receive clearly explained findings with evidence, severity and affected application areas.
Remediation Support
Help engineering teams understand and address identified issues before verification testing.
How Our Penetration Testing Process Works
Discovery
Meet the stakeholders to understand the current testing methodology.
Planning
Prepare a test roadmap based on the targeted application and business.
Development
Conduct a vulnerability assessment to identify security gaps via tests.
Testing & monitoring
Submit a report on findings and suggestions to mitigate threats.
Maintenance & support
Establish a continuous testing policy to identify future risks.
Power Your Project with Security Penetration Testing Services
Security Penetration Testing Services Engagement Models
Why Choose Virtual Coders for Penetration Testing?

"Game-Changing Custom SaaS Solutions – Highly Recommended! Working with Virtual Coders to develop our custom SaaS platform was transformative. Their team grasped our unique needs and delivered a robust solution, greatly enhancing our operations. Their attention to detail and proactive communication made the process smooth and enjoyable. Highly recommended for Australian companies seeking to enhance their software solutions!"
Rick Giesel
Owner, ICT
Why Virtual Coders for Security Penetration Testing Services?
✓Authorized security testing performed against a clearly agreed scope.
✓Evidence-led findings with risk context and practical remediation guidance.
Frequently Asked Questions

Ready to uncover security risks before they become incidents?
Security testing examines how well an application or system protects its data and functions. Penetration testing goes further by safely attempting to exploit agreed targets, helping teams understand which weaknesses are practically exploitable and what should be fixed first.
Testing may uncover application, API, network, authentication, authorization, configuration, and business-logic weaknesses. The exact coverage depends on the agreed scope, environment, access level, and testing method.
Penetration testing can identify exploitable weaknesses, show their practical impact, support risk-based remediation, and provide evidence for internal security reviews. A useful report explains each finding, its severity, supporting evidence, and recommended corrective action.
Security testing is a broad term covering activities such as reviews, scanning, configuration checks, and secure-development testing. Penetration testing is a focused, authorized exercise in which testers attempt to exploit weaknesses within an agreed scope.
Findings are documented with evidence, risk context, and remediation guidance. The responsible team then addresses the issues, after which targeted retesting can confirm whether the fixes are effective and whether any related risk remains.
SEND US A MESSAGE.

READY TO ACCELERATE YOUR TECH JOURNEY?
Partner with our expert engineers to transform your ideas into scalable, high-performance solutions tailored to your business needs.
OUR OFFICES
India
E-414 to 416, Ganesh Glory 11, Jagatpur Road, Nr. BSNL Office, off. S.G. Highway, Jagatpur, Ahmedabad, Gujarat - 382470
Australia
18, Giancarlo Crescent, Doolandella-4077, QLD, Australia
Canada
20 Meadowglen Pl, Toronto, ON M1H 2Y5